

Full Packet Capture Appliance
Enterprise full packet capture for network security monitoring and forensics: 25-40% lower TCO than legacy platforms, lossless capture at 1Tbps line rates, and multi-year retention on commodity hardware.
Overview of Our
Full Packet Capture Appliance
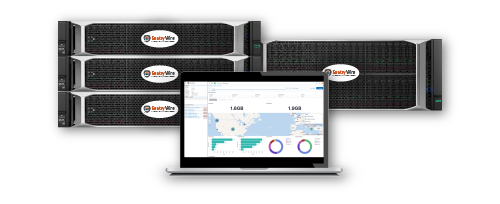
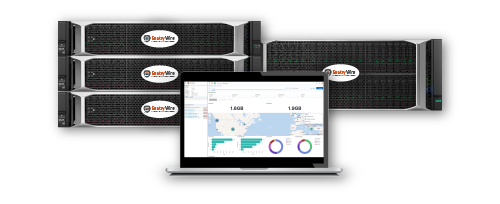
SentryWire's full packet capture appliance is purpose-built for sustained high-throughput ingestion, storage, indexing, and replay across distributed enterprise and federal environments, delivering the performance, scalability, and integration depth required for long-term deployment.
Unlike traditional single-server tools, SentryWire scales compute and storage seamlessly, delivering lightning-fast searches across 100+ PB of network packets. The platform combines high-speed recording with real-time filtering, visualization, and advanced BPF-syntax analysis. Integrated packet analysis functionality and network monitoring dashboards allow teams to investigate suspicious protocols, analyze traffic patterns, and accelerate root-cause analysis.
With extended retention timelines, SentryWire ensures packet data remains available long after most tools have aged out. This matters because state-sponsored intrusions often remain undetected for more than 146 days. Without a high-fidelity packet record, enterprises can’t answer critical questions: when attackers entered, how they moved laterally, or what data was exfiltrated.
Integrates with the security stack you already trust.
Why Network Security Monitoring Requires Enterprise Full Packet Capture
Modern security architectures often rely on logs, flow data, endpoint telemetry, and network detection platforms. While valuable, these technologies provide summaries of network activity and do not preserve complete network packets or packet payloads transmitted across the environment.
Without retained packet capture data, security teams may struggle to determine exactly what entered or exited the network, how attackers moved laterally between systems, what data was transmitted or exfiltrated, and whether intrusion detection alerts accurately reflect underlying activity.
Enterprise full packet capture records complete network packets — headers and payloads — creating a high-fidelity record of network traffic that supports deep forensic analysis and incident response.

The SentryWire Full Packet Capture Architecture
The SentryWire full packet capture appliance is engineered for sustained, enterprise-scale packet recording across distributed networks. Its architecture separates capture, storage, and search functions to maintain performance under high-throughput conditions.
By retaining complete packet data over extended timelines, the platform enables security teams to:
Conduct high-speed retrospective searches across historical packet data
Validate intrusion detection alerts using packet-level evidence
Perform threat hunting across previously captured network sessions
Support forensic investigations with replayable PCAP data
SentryWire complements SIEM, IDS, SOAR, and analytics platforms rather than replacing them. Where those tools summarize behavior, full packet capture preserves the packets that prove what actually occurred.
Unlike single-server systems, SentryWire scales compute and storage horizontally, allowing organizations to expand retention and search capacity without performance degradation.
This design ensures packet capture remains sustainable in federal, regulated, and critical infrastructure environments requiring long-term deployment.
Full Packet Capture
Unlike packet sniffers that only inspect headers or metadata, SentryWire captures complete network packets for forensic replay, deep packet inspection, and long-term analysis.
Powerful & Fast Search
Scale searches with compute and storage, streaming results from PCAP files in near real time without slowing down network performance.
Extended Timeline
Retain network traffic for weeks, months, or even years, ensuring analysts can revisit packet data long after most tools have aged out.
Fast Capture Speed
Capture at line rates from 1Mbps to +1Tbps with lossless performance, even during the burstiest network activity.
IDS Search Back
Use intrusion detection signatures to retroactively search stored packet data, identifying threats that only became known after capture.
Intrusion Detection
Integrated Suricata IDS provides real-time detection and retrospective analysis of suspicious traffic, enabling security teams to validate alerts and investigate threats using packet-level evidence.
Network Operations
Analyze network performance metrics derived from packet data to identify congestion, misconfigurations, and connectivity issues while maintaining a security-first monitoring focus.
Visualization & Analytics
Visualize network traffic and security events through interactive dashboards and Kibana integrations, supporting forensic analysis, anomaly detection, and investigation workflows at scale.
Artifact Extraction
Extract sessionized PCAPs and reconstruct file artifacts from captured traffic to support forensic analysis and evidence-based incident investigations.
Designed for Regulated and High-Consequence Environments
SentryWire is purpose-built for environments where:
Long-term packet retention is mandatory
Compliance mandates require verifiable network evidence
Distributed networks generate sustained high volumes of network traffic
Security monitoring must remain effective over multi-year operational lifecycles
SentryWire delivers this capability on commodity hardware rather than proprietary systems, supporting sustained capture from 1Mbps to over 1Tbps and searches across 100+ PB of packet data, at a total cost of ownership significantly lower than legacy enterprise packet capture solutions.
Ideal deployments include:
Federal government agencies
Defense and regulated public sector organizations
Critical infrastructure and ICS / OT networks
Large enterprises with audit and regulatory obligations
Compliance-Driven Visibility
Enterprise full packet capture supports organizations subject to frameworks such as:
NERC-CIP
SOC 2
HIPAA
SEC 17a-4
By preserving complete packet capture data over extended timelines, organizations can respond to regulatory inquiries with confidence using detailed network packets and forensic analysis rather than partial summaries.
Compliance validation depends on evidence. Full packet capture provides that evidence.
Full Packet Capture vs. NetFlow vs. NDR: At a Glance
| Capability | NetFlow / Flow-Based | NDR / XDR | Traditional Packet Capture | SentryWire |
|---|---|---|---|---|
| Captures full packet payload | ❌ | Limited / on-alert only | ✅ | ✅ |
| Retention timeline | Days–weeks | Days | Days–weeks | Months–years |
| Line-rate capture | N/A | Limited | High, hardware-bound | Up to 1Tbps |
| Scales on commodity hardware | N/A | Varies | ❌ Requires proprietary hardware | ✅ |
| Forensic-grade replay | ❌ | ❌ | ✅ | ✅ |
| Cost per PB retained | Low | N/A | High | 25–40% lower |
| Primary use case | Network performance | Real-time detection | Forensics | Forensics + scale + retention |
Enterprise Use Cases
-
Determining scope, timeline, and impact during an incident requires more than alerts — it requires the underlying packet record that proves what actually occurred.
-
Identifying threats that evaded detection at the time of intrusion depends on access to historical packet data that predates the moment a threat became known.
-
Audit-ready investigations require complete packet payloads, not summaries, to reconstruct sessions and attribute activity with confidence.
-
Alerts without packet-level evidence leave analysts unable to confirm whether a detected event represents a genuine threat or a false positive.
-
Sustained visibility across distributed environments requires a historical packet record that persists beyond the retention windows of logs, flows, and endpoint telemetry.
Additional Platform Capabilities & Integrations
Software Updates: Continuous enhancements keep the full packet capture appliance aligned with evolving threats.
File Hashing: Extract and reconstitute file artifacts from packet captures via the Web UI.
JA3 Hashing & Threat Enrichment: Identify encrypted stream IOCs without decryption.
GeoIP & ASN Enrichment: Enrich metadata logs with location insights.
Enhanced Analytics via Kibana: Build dashboards for traffic anomalies and trends.
Statistical Baselining: Elastic-based analytics detect anomalies in network performance automatically.
Network Operations Analytics: In-browser packet analysis supports investigation of anomalous traffic patterns and network behavior.
Key Considerations for Deploying Full Packet Capture at Scale
Full packet capture provides unmatched visibility for security and forensic investigations and requires careful architectural consideration when deployed at enterprise scale. SentryWire is designed to address the operational challenges that have historically limited the practicality of packet capture in large and regulated environments.
Comprehensive Visibility
The appliance retains complete packet data across north–south and east–west traffic, enabling replayable reconstruction of network activity. This level of visibility supports forensic investigation, threat hunting, incident response, and compliance validation using authoritative packet-level evidence.
Storage Efficiency and Long-Term Retention
Traditional packet capture systems struggle with storage costs and retention limits. SentryWire’s distributed architecture enables long-term packet retention using commodity hardware, allowing organizations to preserve weeks, months, or years of packet data without excessive storage overhead.
Search Performance at Scale
Large PCAP datasets are historically slow to analyze. SentryWire scales search alongside compute and storage, streaming results in near real time so analysts can investigate incidents and perform retrospective analysis without delays.
Operational Complexity
Raw packet data can be difficult to interpret without the right tooling. SentryWire integrates visualization, analytics, IDS search-back, and artifact extraction to streamline investigations and reduce the manual effort required to reconstruct events.
FAQs
-
A full packet capture appliance is a dedicated platform that records and retains 100% of network traffic, including complete packets, headers and payloads. Unlike basic sniffers, it provides forensic-grade evidence for security investigations, incident response, and compliance.
-
NetFlow and flow-based tools collect metadata summaries — connection times, IP addresses, byte counts — but discard the actual packet payload. Full packet capture retains the complete data stream, enabling forensic reconstruction of exactly what happened on the network. For incident response, threat hunting, and compliance, flow data alone is insufficient because it cannot answer what was said, only that a conversation occurred.
-
A packet sniffer typically samples or inspects limited traffic in real time, while a full packet capture appliance records all packets continuously, enabling long-term retention, full replay, and forensic analysis.
-
Full packet capture appliances are most critical in environments where compliance mandates, forensic readiness, and long-term network visibility are non-negotiable. Primary verticals include federal government agencies, defense, and critical infrastructure operators — particularly those running ICS/OT networks subject to frameworks like NERC-CIP and OMB M-21-31. Large enterprises in finance and healthcare with strict retention and audit requirements also rely on full packet capture where flow-based monitoring tools are insufficient. The defining factor is not organization size. It is the consequence of incomplete network visibility.
-
A full packet capture appliance supports network security monitoring by recording and retaining complete packet data across the network. This packet-level visibility enables security teams to investigate incidents, perform threat hunting, validate alerts, and conduct forensic analysis using an authoritative historical record.
-
Full packet capture supports compliance with frameworks that require long-term network visibility and verifiable audit trails, including OMB M-21-31, CDM, NERC-CIP, SOC 2, HIPAA, and SEC 17a-4. Unlike flow-based tools, it retains complete packet data, not summaries or metadata, giving auditors and regulators forensic-grade evidence and letting organizations demonstrate control effectiveness.
-
NDR and XDR platforms analyze behavioral signals and generate alerts, but typically do not retain raw packet data. Full packet capture fills that gap by providing the underlying packet evidence needed to validate alerts, reconstruct attacks, and conduct forensic investigations. Together, they give security teams both real-time detection and the historical record required to investigate what NDR or XDR flags.
-
During an incident, investigators rely on preserved packet data to determine how an intrusion occurred, which systems were affected, and what data may have been accessed or exfiltrated. Full packet capture enables retrospective analysis long after other monitoring systems have aged out their data.
See Full Packet Capture in Action
Free, 60-Minute Demo
Get a tailored walkthrough of full packet capture, real-time filtering, long-term retention, and integrations with Splunk, Elastic, and your existing SIEM. No obligation. Built around your environment, your compliance mandates, and your visibility gaps.
✓ Free, no obligation
✓ 60 minutes, tailored to your environment
✓ Response within 1–2 business days